
Target Audience: SuiteCRM System Administrators, CTOs, IT Security Directors, Operations Leads
Severity: CRITICAL (CVSS 9.2+)
Exploitation Status: Active Automated Exploitation Detected Globally
If your enterprise relies on SuiteCRM to govern customer intelligence, sales pipelines, contracts, and confidential financial workflows, your infrastructure is facing an urgent external threat.
Security researchers have disclosed two devastating zero-day vulnerabilities inside the PHP runtime core: CVE-2026-109618 and CVE-2026-109619 (widely termed the “PHP2Shell” vector).
Compounding this threat, automated threat actors are unleashing autonomous AI scanning agents. These specialized bots sweep public IP ranges, identify exposed CRM endpoints, induce memory corruption in the PHP engine, and achieve unauthenticated Remote Code Execution (RCE)—taking over the server without requiring any administrative credentials or user intervention.
If your organization is running an older SuiteCRM version (such as SuiteCRM 7.8 through 7.13, or early 8.x releases), your backend is likely running on an end-of-life PHP runtime. Here is the breakdown of the danger and how to insulate your business.
The Anatomy of the Threat: CVE-2026-109618 & CVE-2026-109619
These vulnerabilities target the memory management routines of PHP worker processes:
- Out-of-Memory (OOM) Corruption (CVE-2026-109618): Maliciously structured multipart HTTP form submissions force memory allocation limits to trigger abruptly. PHP’s cleanup handler attempts to release structures that were left half-initialized, executing corrupted memory pointers and granting attackers full shell execution as the web-server user.
- Use-After-Free via Stale Worker State (CVE-2026-109619): In persistent worker architectures (such as
mod_phpor pooledphp-fpm), internal pointers referring to already freed memory persist across request lifecycles. AI scanning tools send tailored follow-up queries that trigger this stale state to redirect memory flow.
Why Outdated SuiteCRM Installations Are Prime Targets
The structural overlap between legacy SuiteCRM setups and these PHP flaws creates an immediate exposure window:
- The Unpatched PHP Trap: The PHP core maintainers do not backport security patches to deprecated runtimes. Versions 5.4 through 8.1 are permanently unpatched. If your SuiteCRM is running on PHP 7.3, 7.4, 8.0, or 8.1, your server cannot be patched against these CVEs without a runtime upgrade.
- SuiteCRM 7.x Legacy Codebases: Millions of operations still depend on SuiteCRM 7.x. However, versions prior to 7.14 are tied to PHP 7.x or 8.0, making them incapable of running on modern, secured PHP releases without code updates.
- AI-Assisted Fingerprinting: Unlike random DDoS traffic, modern AI scanning tools recognize SuiteCRM directory structures (
/index.php?entryPoint=...,/custom/, entry forms) in milliseconds and systematically execute memory-amplification attacks against them.
Supported vs. Vulnerable Matrix: Where Your Stack Must Be
Check your hosting server’s PHP binary and SuiteCRM build against the baseline matrix:
| SuiteCRM Branch | Required PHP Version | PHP Security Status | Action Required |
|---|---|---|---|
| SuiteCRM 7.0 – 7.13 | PHP 5.5 – 7.4 / 8.0 | PERMANENTLY VULNERABLE | Urgent Migration Required |
| SuiteCRM 7.14 / 7.15 (LTS) | PHP 8.2 / 8.3 / 8.4 | Secure (if on 8.2.35+, 8.3.36+, 8.4.27+) | Update PHP point release |
| SuiteCRM 8.0 – 8.3 | PHP 7.4 / 8.0 / 8.1 | PERMANENTLY VULNERABLE | Upgrade SuiteCRM core & PHP |
| SuiteCRM 8.4 – 8.7+ | PHP 8.2 / 8.3 / 8.4 | Secure (if on 8.2.35+, 8.3.36+, 8.4.27+) | Update PHP point release |
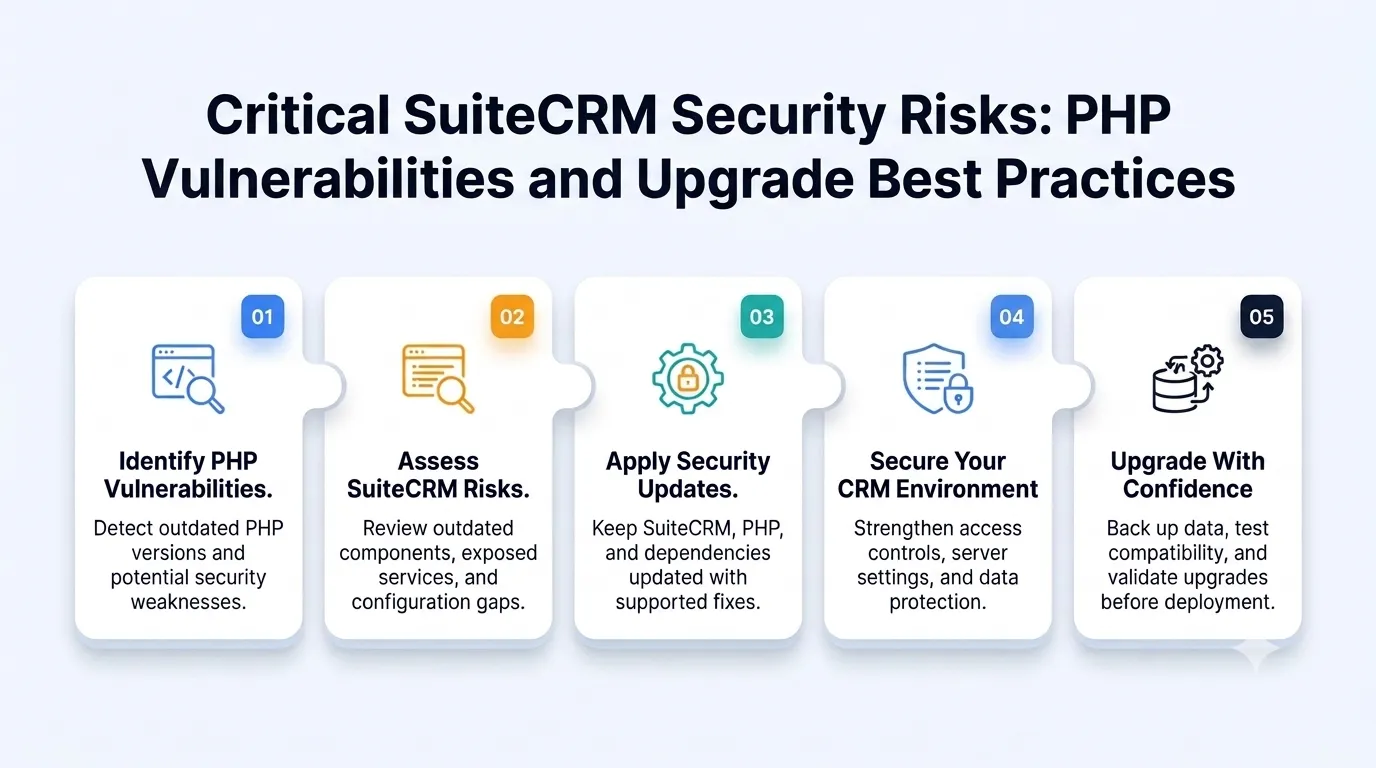
Emergency Defensive Mitigations for IT Administrators
If you cannot migrate your CRM instance today, apply these immediate protective controls to blunt automated bot incursions:
1. Enforce Strict Memory & Upload Limits (php.ini):
- Dramatically reduce upload thresholds to eliminate large allocation triggers:
Ini, TOML
Plain Text
post_max_size = 16M
upload_max_filesize = 16M
session.upload_progress.enabled = 0- Restart
php-fpmor web services immediately to clear persistent worker memory pools.
2. Enforce Perimeter Access Control:
- Isolate the SuiteCRM administrative and entrypoint URLs behind an authenticated corporate VPN or a strict IP allowlist. Do not leave the administrative console publicly discoverable to global indexing bots.
3. WAF Layer Request Inspection:
- Configure Web Application Firewall (WAF) inspection rules to throttle rapid multipart POST bursts and block irregular zero-length or oversized chunked requests.
Upgrade Without Disruption: Free Consultation by Variance Team
Modernizing an enterprise SuiteCRM environment is rarely straightforward. Custom logic hooks, custom modules built in Studio, complex database relationships, and third-party integrations (telephony, payment gateways, marketing tools) often break when jumping PHP versions:
- Will custom workflows or workflows built on SugarBeans fail under PHP 8.2+?
- Can you safely upgrade from SuiteCRM 7.x to 8.x without corrupting legacy data?
- How can you achieve this modernization with zero downtime for your sales force?
The Variance team possesses deep, hands-on engineering experience modernizing enterprise CRM platforms, refactoring custom extensions, and securing open-source backend stacks.
To safeguard your business against active exploits, we are offering a Free SuiteCRM Security & Upgrade Assessment:
- Vulnerability & Architecture Audit: We verify your PHP runtime build, analyze server worker behavior, and isolate exposure to CVE-2026-109618/CVE-2026-109619.
- Custom Module & Hook Compatibility Scan: We test your custom modules, API integrations, and legacy customizations against PHP 8.x syntax and modern SuiteCRM cores.
- Risk-Free Staging & Migration Plan: We construct a step-by-step roadmap using isolated staging environments and validated database migrations—guaranteeing complete data integrity with zero business downtime.
Secure Your Customer Data Before Attackers Strike
Do not leave your critical CRM infrastructure exposed to automated exploitation. Partner with the Variance team to audit, patch, and modernize your environment today.
Book Your Free SuiteCRM Security Audit with the Variance Team
Confidential. Comprehensive. Completely free of obligation.
 Please wait...
Leave a Reply