
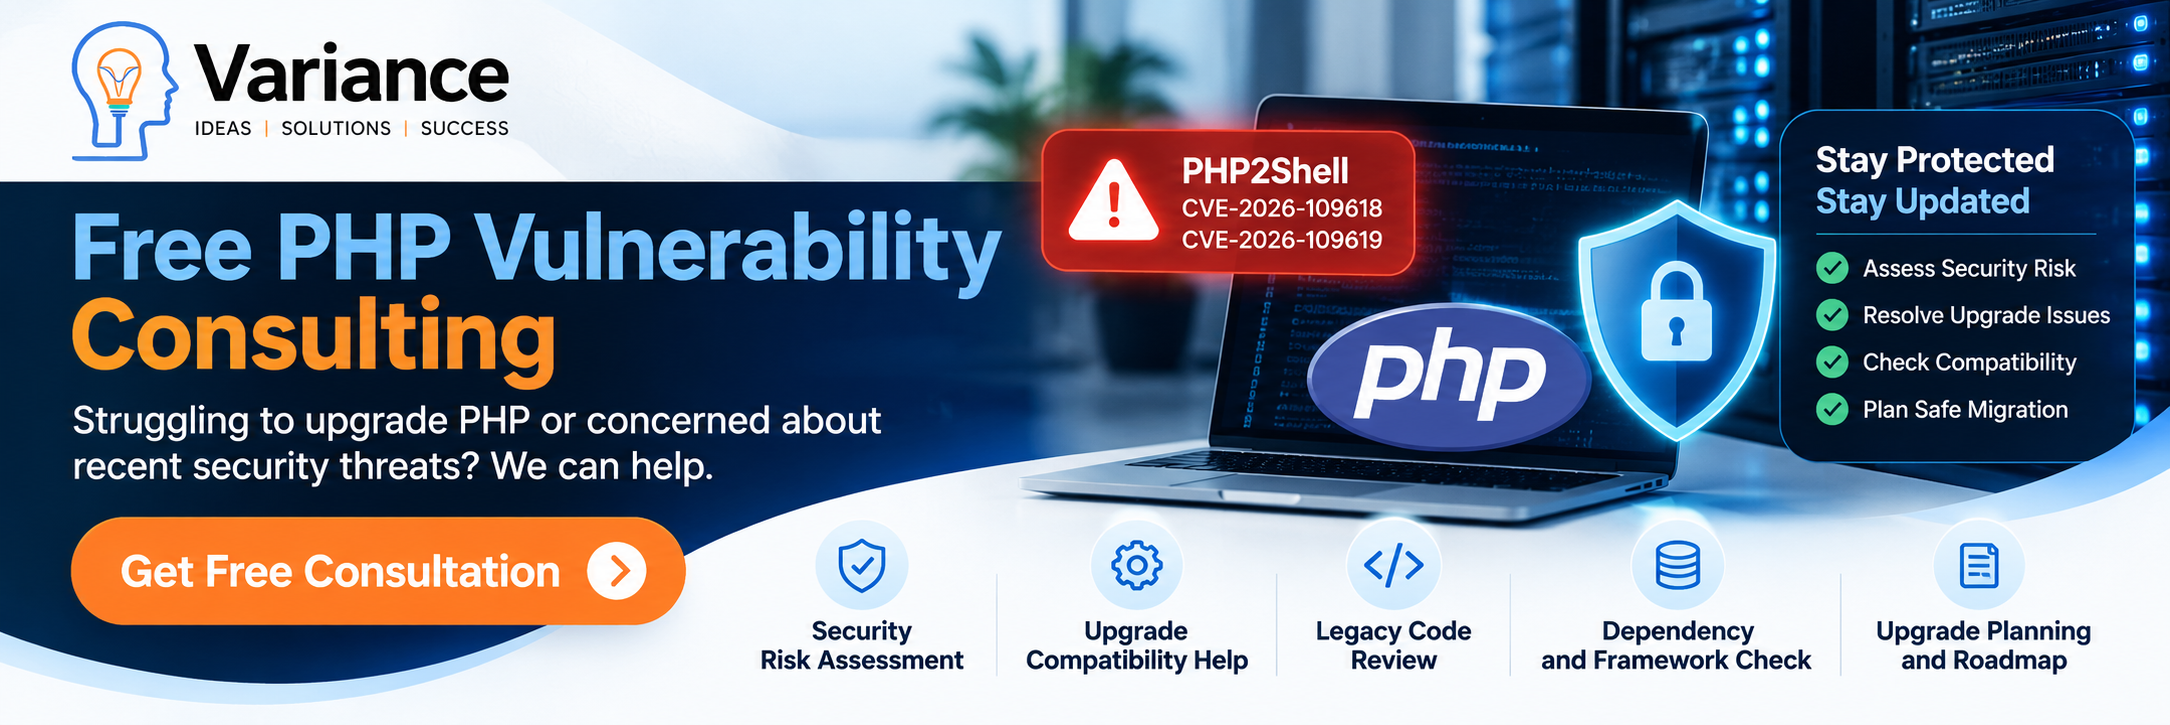
The PHP ecosystem is facing an important security issue following the disclosure of two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, also discussed under the name PHP2Shell.
These vulnerabilities can potentially allow attackers to execute code remotely without authentication under vulnerable conditions. The PHP development team has released security updates and strongly recommends that administrators update affected installations immediately.
The security-fixed releases are PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. PHP 8.1 and older versions no longer receive updates directly from the PHP project, making it particularly important for businesses running legacy applications to verify their protection and upgrade options.
Official reference: PHP Security Advisory
Why Is This a Challenge for Businesses With Legacy PHP Applications?
For many organizations, applying a security update is not as simple as installing a new PHP version. Their applications may depend on old frameworks, custom code, third-party integrations, or libraries that have not been tested against newer releases.
Common upgrade blockers include:
- Critical application features failing after a PHP version change.
- Deprecated or removed functions causing runtime errors.
- Composer dependencies that prevent installation of a supported PHP version.
- Older frameworks that require substantial changes before migration.
- Uncertainty about whether a patch can be applied safely without downtime.
- Limited testing environments and concerns about production stability.
Delaying an update can leave a business exposed, but making an untested change can also disrupt critical workflows. The right approach is to identify the affected runtime, verify available security fixes, assess compatibility, and plan a controlled upgrade.
Get Free PHP Vulnerability Consulting
If your organization is struggling with PHP security updates or cannot upgrade its legacy application, we invite you to request a free initial PHP vulnerability consultation.
We can help you discuss:
- Your current PHP version and security concerns.
- Whether your hosting provider has applied the relevant security patches.
- Compatibility issues preventing an upgrade.
- Legacy dependencies and framework limitations.
- A practical remediation and migration roadmap.
The objective is to help you understand your exposure and decide on appropriate next steps before proceeding with a larger upgrade project.
Don’t let legacy code prevent you from addressing important security updates.
Contact us to discuss your PHP upgrade challenges and explore a safer path forward.
CTA: Request Your Free PHP Security Consultation
Note: The initial consultation is not a comprehensive security audit or a guarantee that all vulnerabilities will be discovered. Detailed code reviews, penetration testing, and remediation can be scoped separately.
 Please wait...
Leave a Reply